kodesec/security
Vulnerability Assessment
Broad infrastructure scanning with manual verification, so you get a prioritised list of real issues — not noise.
Problems we solve
Is this you?
Scanner output is thousands of lines and nobody knows where to start
Patching is reactive and nothing is prioritised by real risk
Compliance requires regular vulnerability assessments
What's included
Everything in this service
- Infrastructure vulnerability scanning
- Manual verification
- Risk prioritization
- Remediation roadmap
Process
How the engagement runs
- 01
Scope
Agree targets, rules of engagement, test windows and success criteria.
- 02
Recon & mapping
Enumerate the attack surface — apps, APIs, hosts, identities and cloud assets.
- 03
Manual testing
Exploit and chain vulnerabilities by hand, guided by OWASP, PTES and MITRE ATT&CK.
- 04
Report
Risk-rated findings with proof, business impact and step-by-step remediation.
- 05
Re-test
Verify every fix and issue an updated report you can share with customers and auditors.
Deliverables
What you receive
- Executive summaryA one-page view of risk for leadership and customers.
- Technical reportReproducible findings with CVSS scores, evidence and remediation.
- Re-test letterConfirmation that fixed issues are closed — ready for audits and due diligence.
Benefits
Why teams choose Kodesec
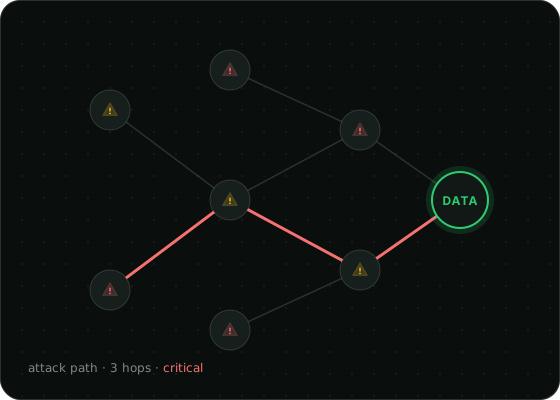
- Real exploits, not theoretical risksWe chain findings the way attackers do — so you see which weaknesses can actually be weaponised, not a list of 400 scanner alerts.
- Business logic, tested by handAuthorisation flaws, IDORs and workflow abuse don't show up in scanners. Senior testers look for them manually, on every engagement.
- Fixes you can ship, then verifyEvery finding comes with a reproducible proof, a plain-language impact and a fix path — and we re-test it once you've patched.
Technologies
Tools & platforms
- Burp Suite
- Nmap
- Metasploit
- BloodHound
- Nuclei
- OWASP ZAP
- ScoutSuite
- Prowler
- Wireshark
FAQ
Questions, answered
How is this different from an automated scan?
Scanners find known patterns. Our testers think like attackers — chaining low-risk issues into real impact and testing the business logic that tools can't understand.
Will testing disrupt production?
No. We agree safe test windows and rules of engagement up front, avoid destructive techniques, and can test staging environments instead.
Do you sign an NDA?
Yes — before any technical detail is shared.
More in Cybersecurity
Related services
Web Application Penetration Testing
OWASP-aligned manual testing of your web apps and APIs — authentication, authorisation and the business logic scanners miss.
Learn moreNetwork Security Testing
Internal and external network assessments, including Active Directory attack paths and privilege escalation.
Learn moreCloud Security Assessment
Configuration and IAM reviews of AWS, Azure and GCP against CIS benchmarks and real attacker techniques.
Learn moreMalware Detection & Investigation
Analyse suspicious files and systems, find persistence and indicators of compromise, and contain the incident.
Learn moreSecurity Consulting
Roadmaps, risk assessments and architecture reviews that turn security into a plan your team can actually execute.
Learn more
Talk to us about vulnerability assessment
A free 30-minute scoping call with an engineer. Fixed quote within 48 hours.
Book a call