Incident Overview
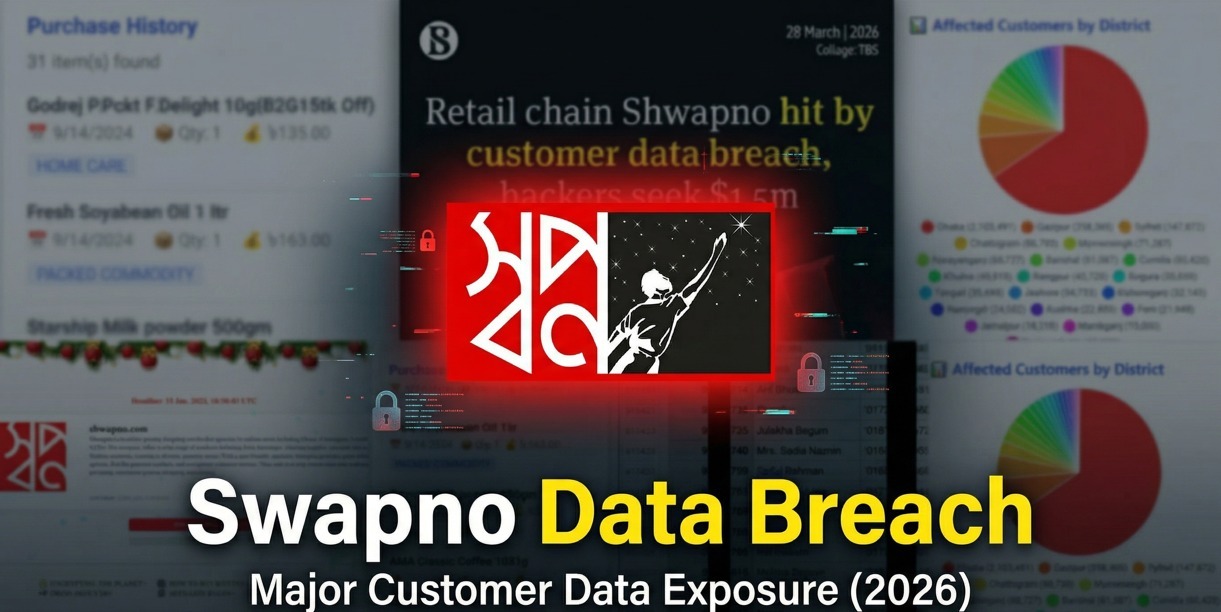
In March 2026, Shwapno, one of Bangladesh’s largest retail chains operated by ACI Logistics Limited, suffered a major data breach impacting approximately 4 million customers across 63 districts.
The attack has been reportedly linked to ransomware groups such as LockBit and Qilin, both known for sophisticated double-extortion tactics, based on public sources.
The attackers demanded a ransom of $1.5 million USD, which the organization reportedly declined. As a result, portions of the stolen data were leaked and circulated on underground forums and social platforms.
What Happened: Breach Breakdown
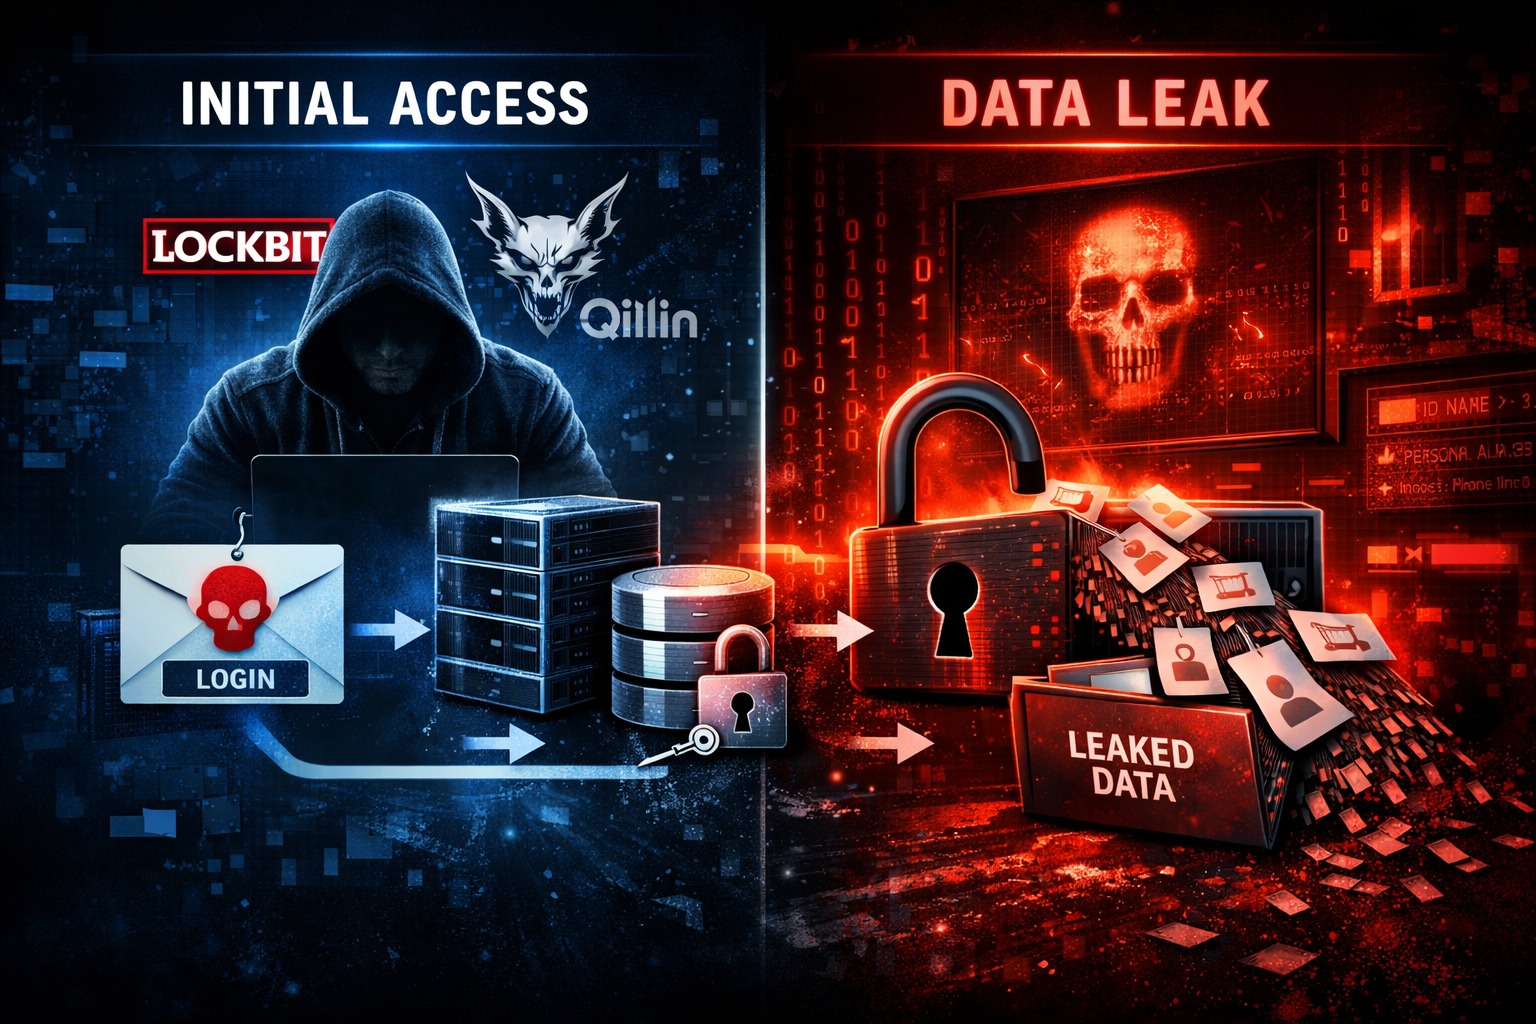
The attack was not a single event but a multi-stage intrusion campaign:
- Initial Access (August 2025): Attackers launched targeted phishing campaigns against employees. Malicious links were delivered, potentially leading to credential compromise and malware execution.
- Foothold & Lateral Movement: After initial compromise, attackers navigated internally due to weak segmentation, gradually moving toward critical infrastructure.
- Dwell Time (August–December 2025): The attackers remained undetected for over 90 days, significantly exceeding commonly reported global averages for dwell time.
- Database Compromise (December 2025): Reports suggest attackers may have gained extensive access to customer databases.
- Ransom Demand & System Disruption: Internal systems became inoperable, and ransom was demanded with a strict deadline.
- Data Leak (March 17–18, 2026): After refusal to pay, attackers publicly released sensitive customer data.
- Delayed Disclosure (March 29, 2026): A General Diary (GD) was filed months after initial compromise, which has raised discussions in the cybersecurity community regarding response timelines.
Compromised Data
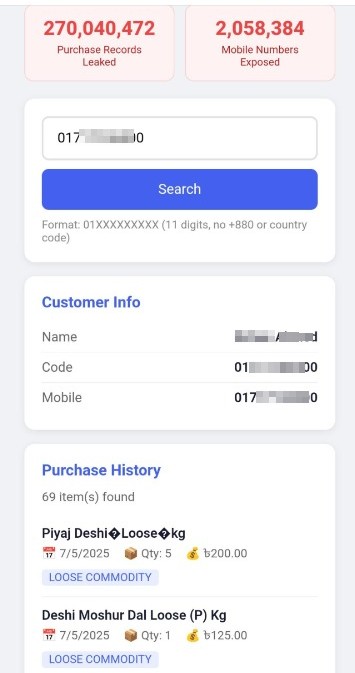
The breach exposed sensitive personal and behavioral data:
- Full Names
- Mobile Phone Numbers
- Purchase Histories (2025 transactions)
While financial transaction systems were reportedly isolated, the exposed dataset is highly valuable for social engineering and fraud campaigns.
Impact Analysis
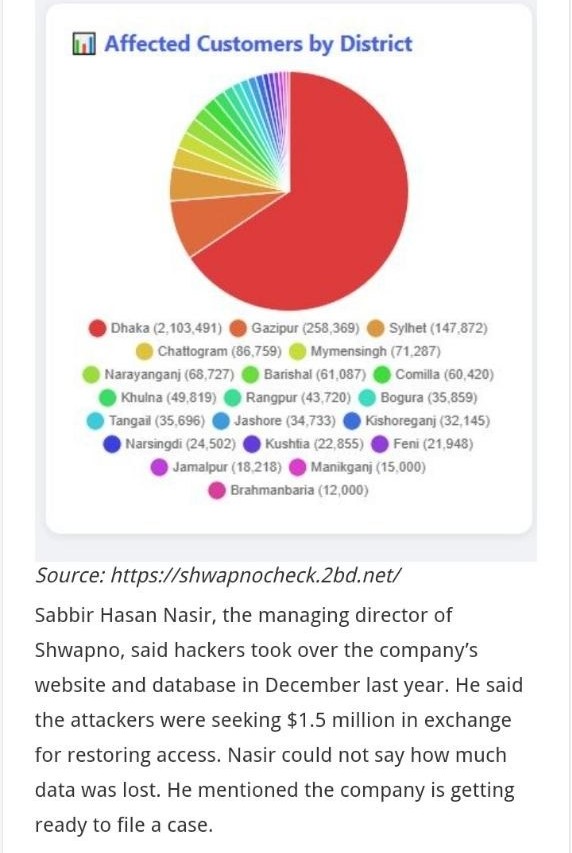
The breach had a nationwide footprint, with concentration in urban areas:
- Dhaka: 2.1 million+ affected users
- Gazipur, Sylhet, Chattogram: Significant exposure
- Coverage across 63 districts
This scale makes it one of the largest consumer data breaches in Bangladesh.
Root Causes: Why This Happened
The incident appears to reflect multiple potential cybersecurity gaps:
- Detection Failure: Possible absence or misconfiguration of robust EDR/XDR solutions may have contributed to delayed detection.
- Poor Network Segmentation: Flat network architecture enabled attackers to move laterally from user endpoints to core databases.
- Phishing Susceptibility: Employees were not adequately trained to identify targeted phishing attacks.
- Weak Incident Response: Delayed response beyond commonly recommended early-response timeframes.
- Legacy Security Gaps: Past publicly reported incidents may indicate ongoing security challenges.
Company Response
According to public disclosures:
- Refused ransom payment based on ethical policy.
- Engaged law enforcement including CTTC.
Deployed:
- Next-generation firewalls
- Endpoint protection systems
- Continuous monitoring solutions
- Conducted internal audits via MIS teams
- Claimed operational systems are partially offline-isolated
Note: The timing of disclosure and response has been noted as a point of concern in public discussions.
Key Contradictions
- Attackers claim full access and ransom demand in August 2025.
- Organization claims awareness of full impact much later.
This discrepancy may indicate potential visibility gaps or delayed escalation, which are common in advanced persistent threats (APTs).
How This Could Have Been Prevented
At KodeSec, we analyze incidents like this to highlight preventable gaps. A breach of this scale typically requires multiple control failures—not just one.
Critical Preventive Measures
- Zero Trust Architecture: Strict identity verification and least-privilege access could have limited lateral movement.
- Advanced EDR/XDR Deployment: Real-time behavioral detection would have identified unusual privilege escalation, lateral movement, and data exfiltration patterns.
- Security Awareness Training: Simulated phishing campaigns and continuous employee training reduce human risk.
- Network Segmentation: Separating user endpoints, application servers, and customer databases prevents full-system compromise.
- Immutable Backups: Offline, tamper-proof backups ensure business continuity without ransom dependency.
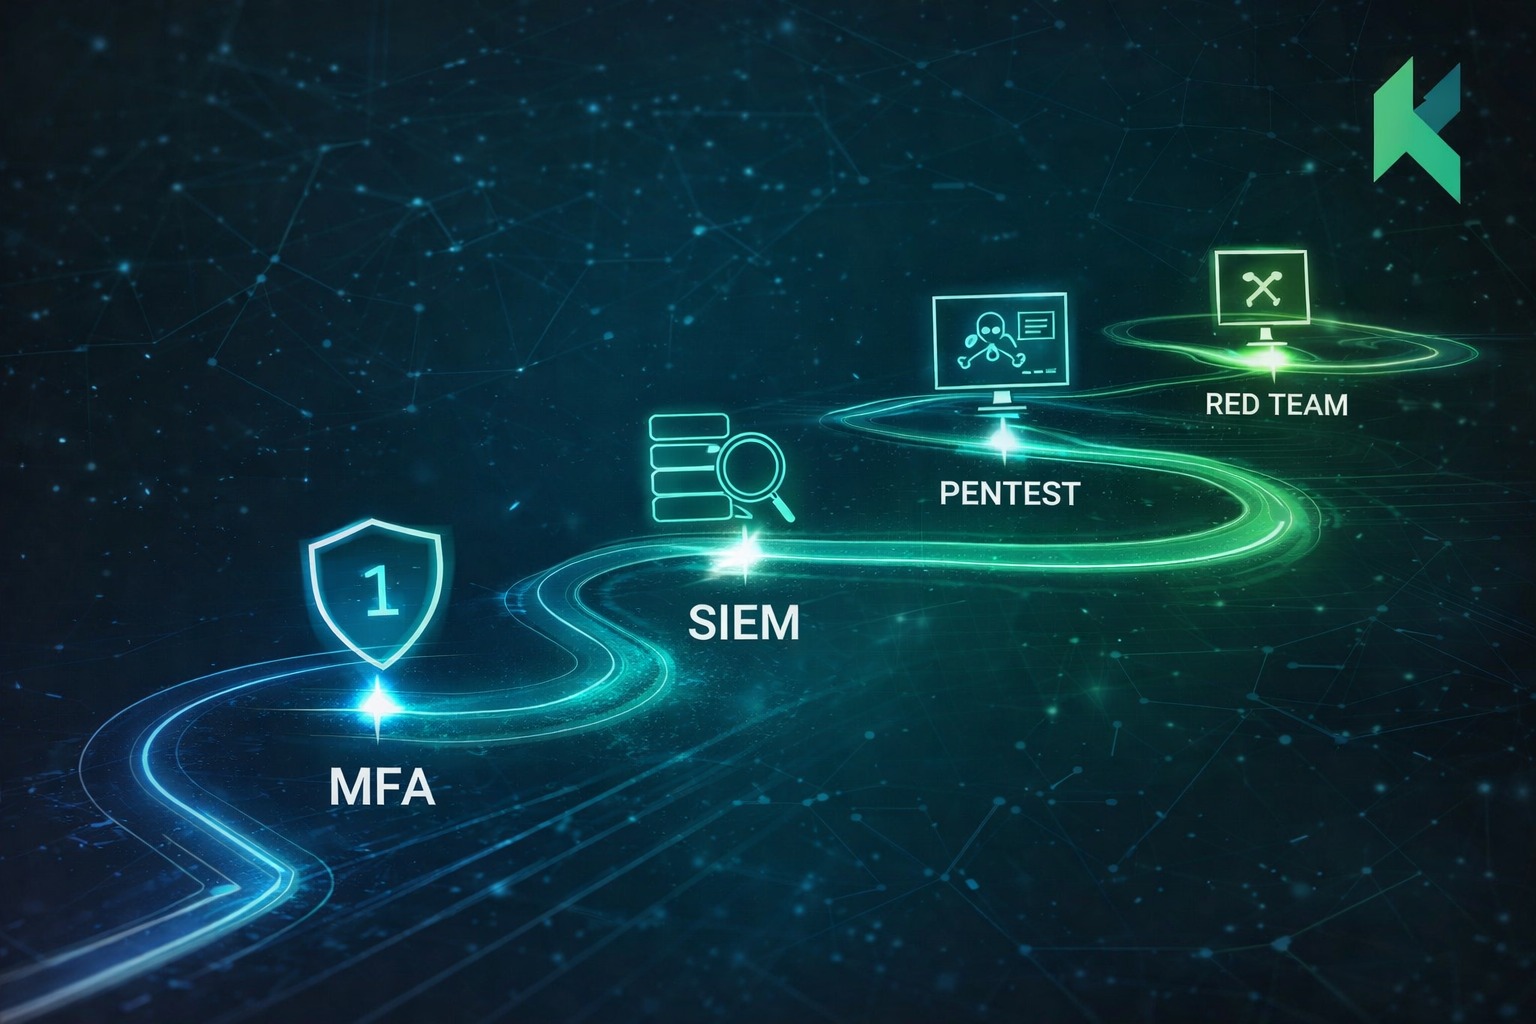
- Continuous Penetration Testing: Regular web application testing, Active Directory assessments, and cloud security audits help identify exploitable weaknesses before attackers do.
How Kodesec Can Help
Security-focused partners, such as KodeSec, aim to reduce risk and impact through proactive security practices. Our approach includes:
- Secure Infrastructure Design (on-premise and cloud)
- Secure Software Engineering and DevSecOps integration
- Offensive Penetration Testing and internal network assessments
- Cloud penetration testing and misconfiguration audits
- Quality Assurance & E2E Validation
- Incident response planning and tabletop simulations
We focus not only on preventing breaches but also on significantly reducing attacker dwell time through improved detection and response capabilities.
Recommended Security Roadmap for Organizations
To prevent similar breaches in the future:
- Enforce Multi-Factor Authentication (MFA) across all systems.
- Deploy SIEM + Threat Intelligence feeds.
- Conduct compromise assessments regularly.
- Implement least privilege access control.
- Monitor and log all critical activities.
- Perform regular red team exercises.
- Maintain incident response playbooks.
Cybersecurity should be treated as a business risk, not just an IT function.
Guidance for Affected Customers
If you are a Shwapno customer, take the following steps immediately:
- Reset Credentials: Change passwords for email, banking, and e-commerce platforms (especially if reused).
- Stay Alert for Phishing: Be cautious of fake promotional SMS, calls claiming to be from Shwapno, or suspicious links.
- Monitor Financial Activity: Even though financial data wasn’t reportedly leaked, remain vigilant.
- Limit Data Exposure: Avoid sharing personal information over phone calls or unknown platforms.
- Use Security Tools: Enable MFA, spam filters, and mobile security apps.
Final Thoughts
The Shwapno breach is not just an isolated incident—it is a notable example of a modern large-scale cyber incident targeting retail infrastructure. It demonstrates that attackers are patient, human error remains a key entry point, and detection speed defines the total damage.
Developing situation. Organizations may consider this an opportunity to reassess and strengthen their cybersecurity posture.
Note: This analysis is based solely on publicly available information and is intended for educational and awareness purposes.
References
- DeXpose: Qilin Targets Retailer Shwapno
- UpGuard: Shwapno Data Breach Analysis
- Beyond Machines: Retail Chain Suffers Data Breach
- The Business Standard: GD Filed Seven Months After Breach
- The Financial Express: Hackers Demand $1.5M Ransom
- #data breach
- #bangladesh
- #ransomware
Written by
Kodesec ResearchResearch team